AI your second line can actually sign off.
Nobody in a regulated firm is short of AI ideas. What stops them is the first slide Risk and Compliance put up: where does the data go, who approved the model, and can you show me the record. StickyPrompts answers those questions with settings you can open and records you can export.
- Staff pasting client data into consumer AI tools because the sanctioned option does not exist yet
- Every new AI tool triggering a fresh third-party risk assessment
- No single record of who used which model, on what, and when
Six things financial services teams use this for.
Not an exhaustive list. These are the ones that come up first, and the ones that make the case for the rollout on their own.
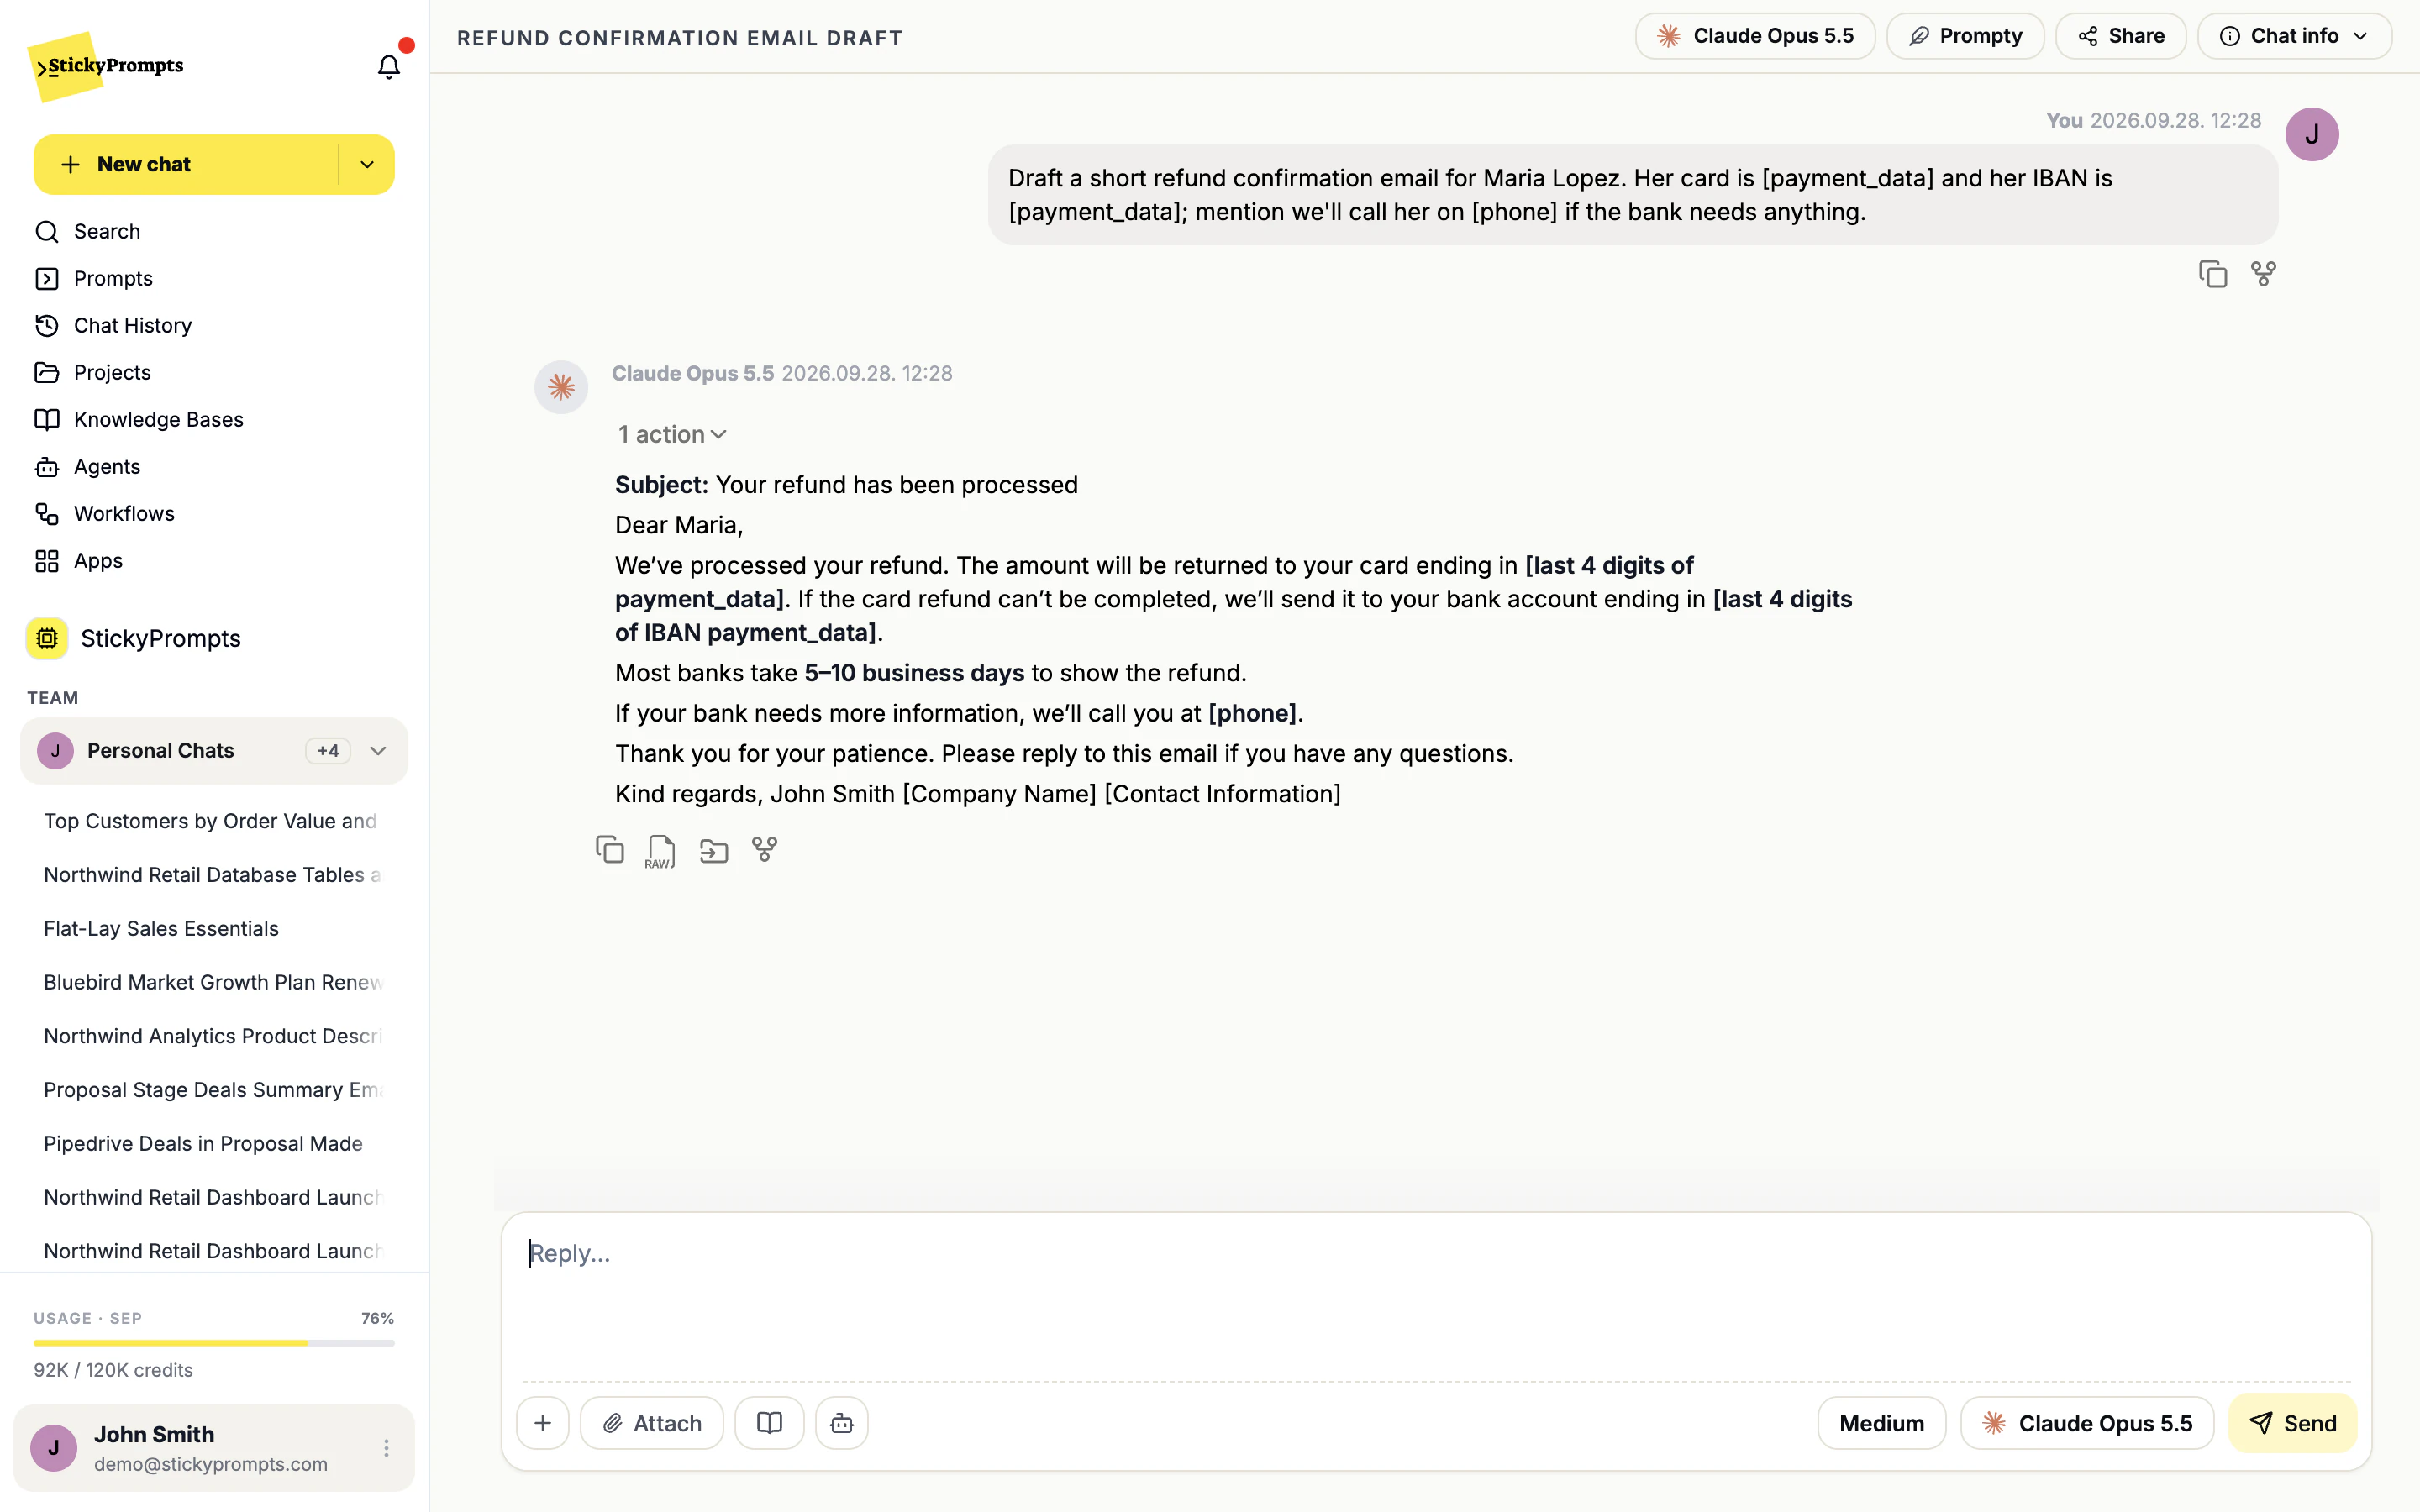
Card numbers never reach the model.
Sensitive info detection catches card numbers, IBANs and phone numbers as they are typed and replaces them before anything leaves the workspace. Every catch is recorded in the privacy log.
See the full product tourApproved providers, and nothing else.
Allow a provider for everyone, block it, or open it to named teams only. Models that cannot meet your data residency settings are greyed out and cannot be used.
See the governance controls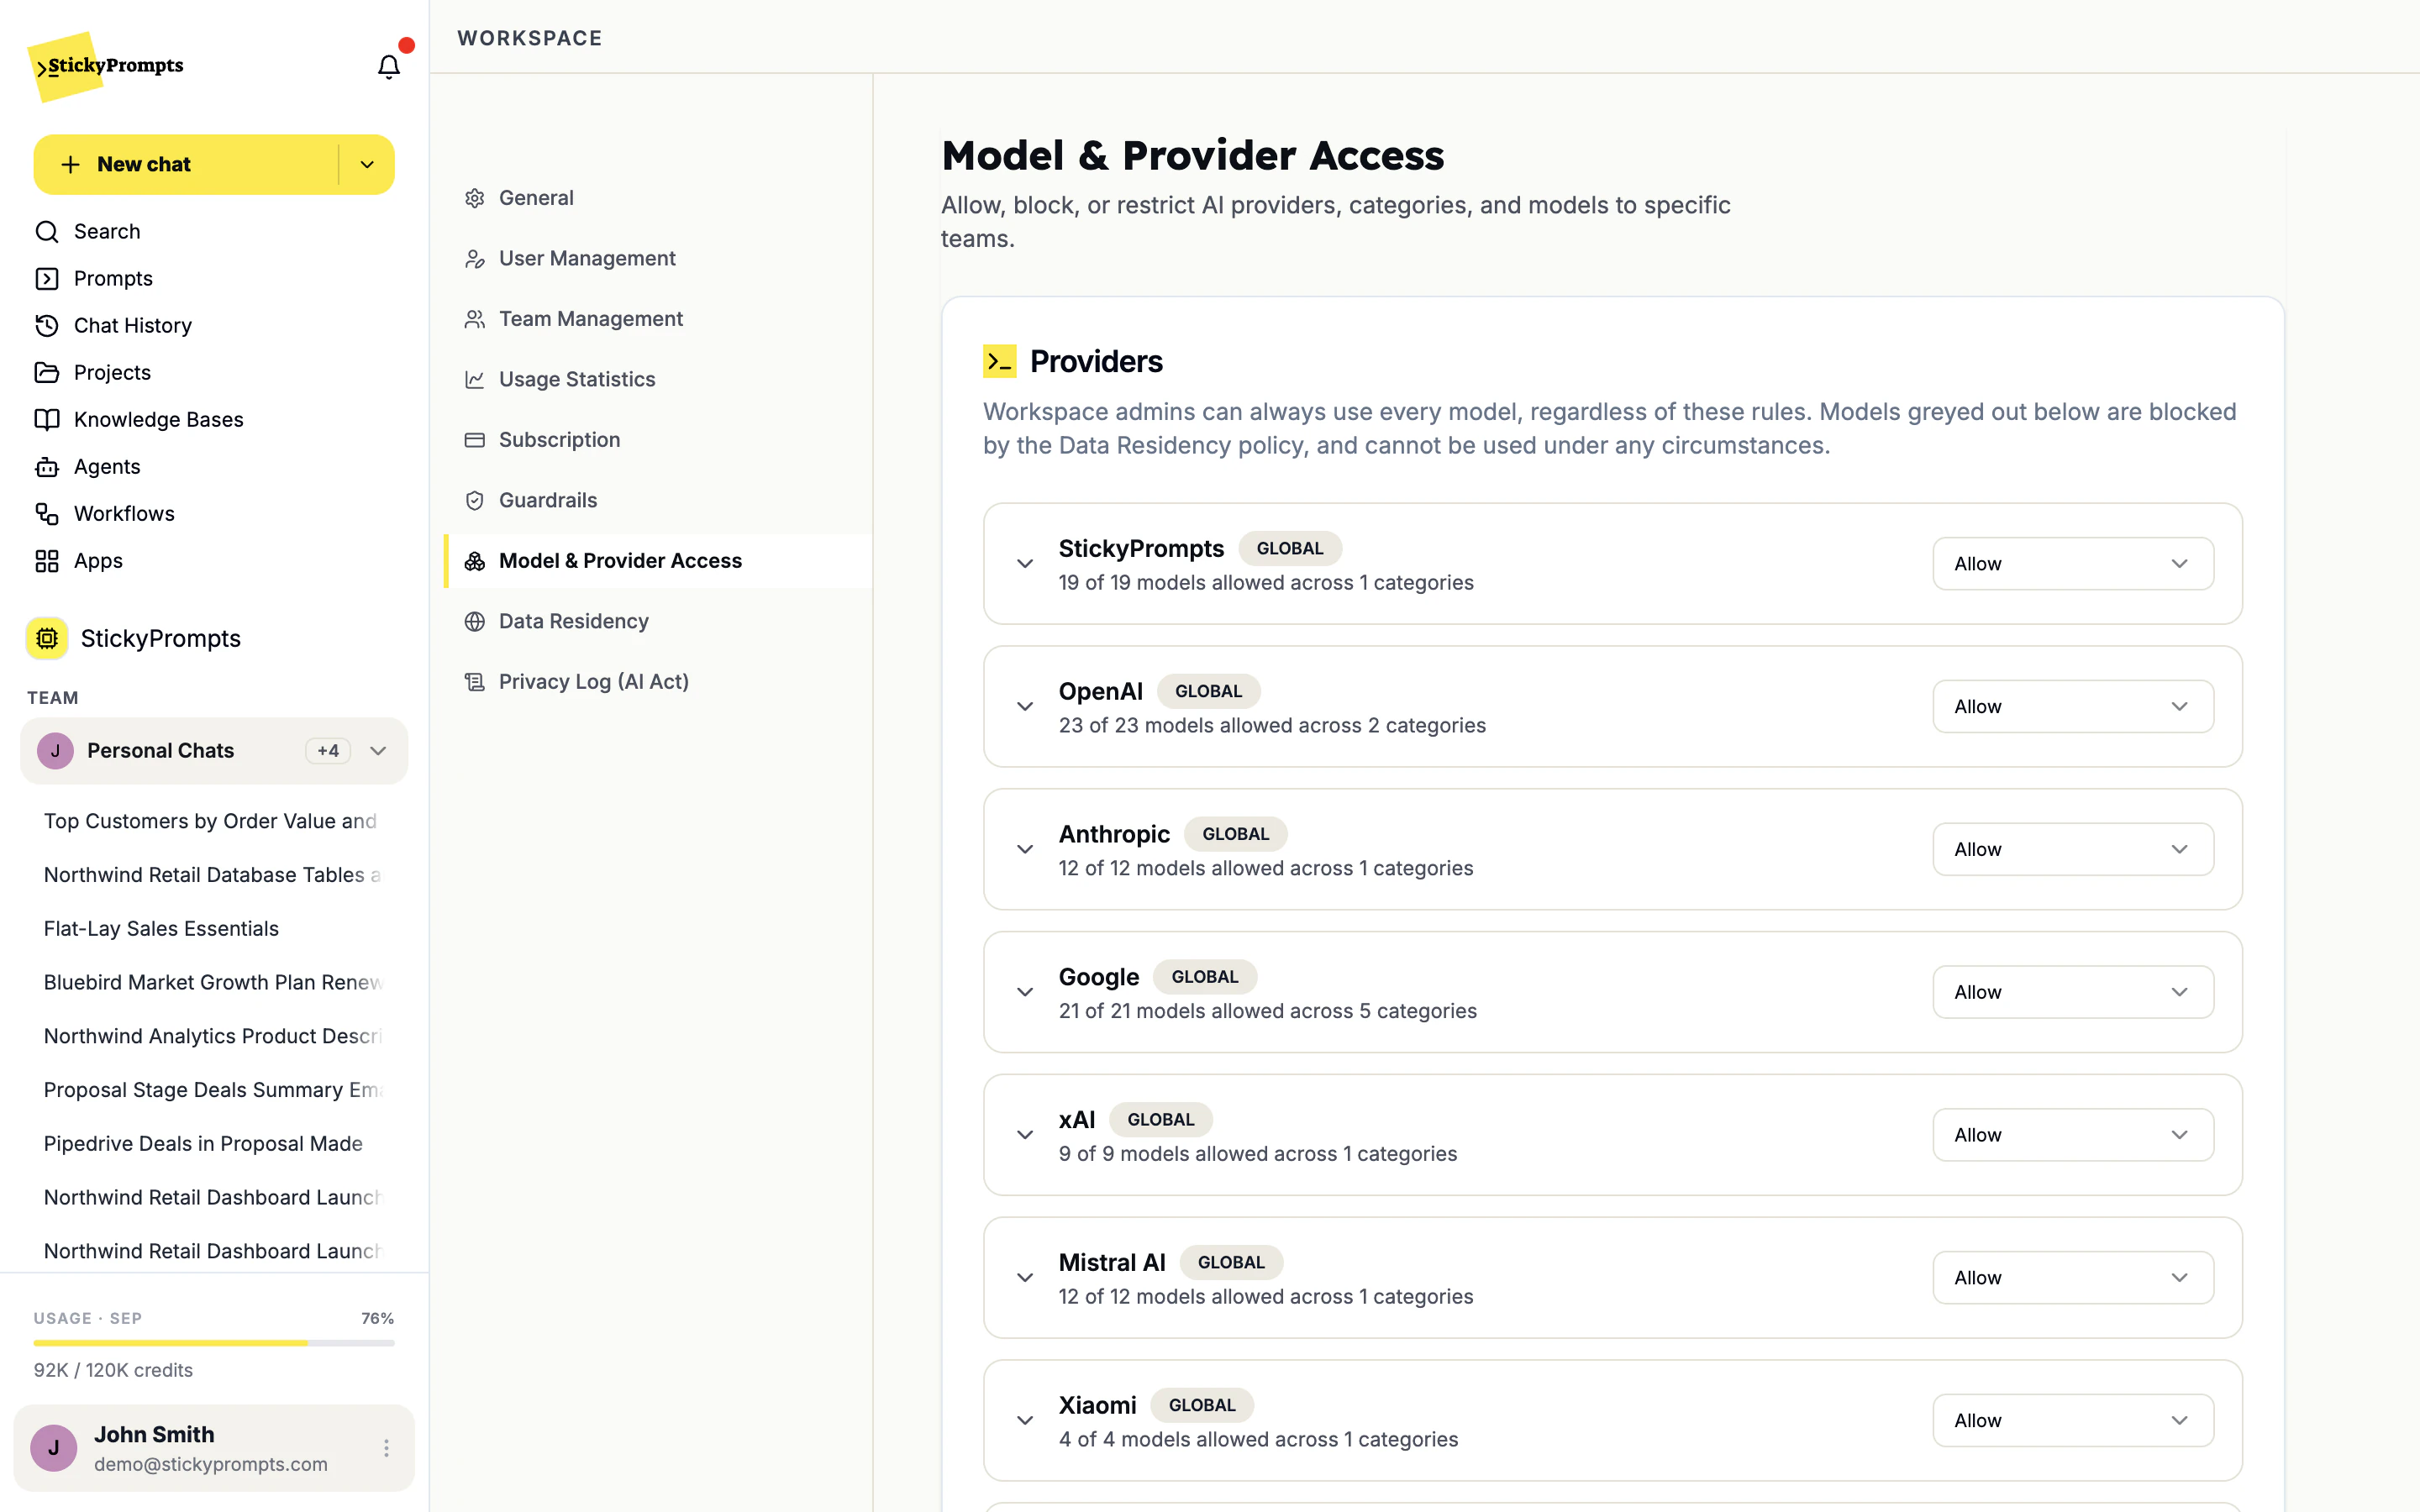
- Card numbers, IBANs and IDs redacted before a prompt reaches any model
- Providers allowed, blocked or opened to named teams only
- Data stored in the EU by default, with EU-served inference as a switch
- Zero-data-retention providers only, if you require it
- A privacy log of every redaction and policy change, with export
- Usage by user, team and model in the workspace statistics
What financial services teams ask us.
Does this make us compliant?
No product can do that, and you should be suspicious of any that claims it. What StickyPrompts gives you is controls and records: sensitive-data redaction, provider access rules, data residency settings and a privacy log you can export. Whether your use of them meets your obligations is a judgement for your own compliance function and regulator.
Can we stop staff using particular models or providers?
Yes. In Model & Provider Access an admin allows a provider, blocks it, or opens it to specific teams only. Models that cannot meet your data residency settings are greyed out in the picker rather than quietly used.
How do we evidence what happened for an audit?
The privacy log records every guardrail trigger (warned, redacted or blocked) and every policy change, with filters and an export. Usage statistics show who used which model and when, by user and by team. Chat history keeps the conversations themselves.
By industry
Try it on your own work before you commit.
Start free with a $5 trial balance. No card, no procurement marathon - bring one real task and see how far it gets.